Disconnected security tools and manual handoffs
Unified security incident orchestration
Security teams drown in alerts — SecOps connects detection, response, and governance.
Disconnected security tools and manual handoffs
Unified security incident orchestration
Alert fatigue with low signal-to-noise ratio
Automated enrichment and prioritization
Slow incident response across siloed teams
Integrated response workflows with ITSM and GRC
No integration between SecOps and ITSM
Threat intelligence driving proactive defense
Compliance gaps in security event handling
Audit-ready security event documentation
Explore how ServiceNow SecOps accelerates detection, response, and recovery.
Module 01
Orchestrate response workflowsfrom detection throughcontainment and recovery.
Module 02
Enrich alerts with threatcontext to prioritize whatmatters most.
Module 03
Prioritize and remediatevulnerabilities based onbusiness risk.
Module 04
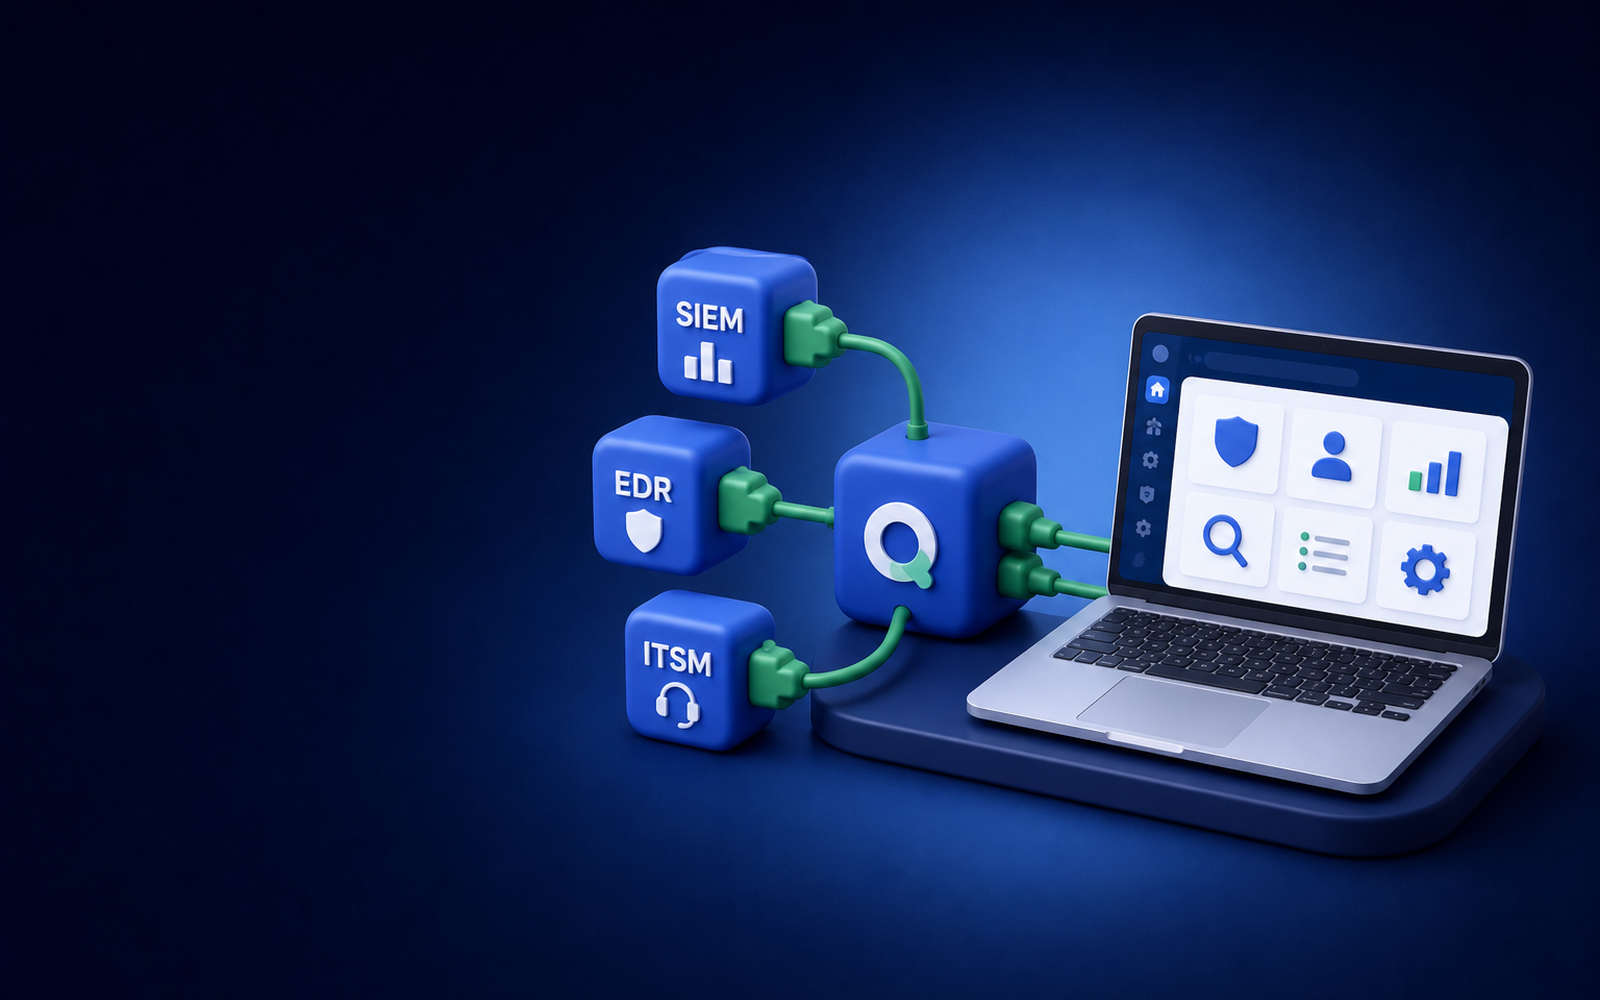
Connect SIEM, EDR, and scanningtools into unified workflows.
Module 05
Automate containment actions toreduce mean time to respond.
Module 06
Executive dashboards andcompliance reporting forsecurity posture.
SecOps integrates with ITSM, GRC, and ITOM — unifying security with business operations.
Quantifiable improvements from integrated SecOps.
Proactive threat detection and response
Integration with GRC and ITSM for unified operations
Automated security incident response workflows
Operational security across the enterprise
Proof clients track with us
Four signals we keep visible across every engagement.
Years of ServiceNow excellence
Certified ServiceNow professionals
Successful implementations
Industries served
Deploy SecOps with your existing security stack.
Phase 01
Map existing tools, playbooks, and SecOps maturity gaps.
How enterprises strengthen their security posture.
Financial Institution
4-hour average security incident response time
Orchestrated playbooks respond in under 45 minutes
70% faster threat response
Technology Company
10,000+ daily alerts with 5% actionable
Intelligent enrichment prioritizes top 200 critical alerts
50% reduction in alert fatigue
Schedule a SecOps assessment — integrate threat response with ITSM and GRC on one platform.
Platform Assessment & AI Readiness
Discuss AI readiness, agentic workflows, and platform goals — and leave with practical guidance tailored to your operating model and roadmap.
Your information stays secure and confidential.